

Dutch law enforcement authorities have apprehended Pepijn van der Stap, a 24-year-old convicted cybercriminal from the Netherlands, on suspicion of providing critical support to the notorious hacker collective known as ShinyHunters. The arrest, which took place on or around September 16, 2026, has triggered a chaotic and retaliatory response from the hacker group, marking a significant escalation in a global cyber-espionage and extortion saga that has compromised major government and private sector entities.
Van der Stap, previously known in underground hacking circles by the alias "Umbreon," has a well-documented history of data theft. His arrest follows a 2023 conviction related to a spree of extortions that yielded between €1.5 million and €2.7 million. Despite serving a prison sentence—from which he was released in December 2025—the suspect had attempted to rebrand himself as a reformed security researcher, even securing employment as an offensive security lead at the Amsterdam-based Neo Security. However, investigators now allege that his dual life persisted, with his expertise being funneled into the infrastructure of ShinyHunters.
The Anatomy of a High-Stakes Cyber Conflict
The timeline of the current escalation began in early 2026, when ShinyHunters successfully infiltrated Odido, the Netherlands’ largest mobile telecommunications provider. By social engineering an employee into accessing a spoofed portal, the group exfiltrated sensitive data belonging to approximately 6.2 million Dutch citizens. Following the incident, Dutch authorities publicly released audio recordings of the attacker, seeking public assistance in identifying the native Dutch speaker.

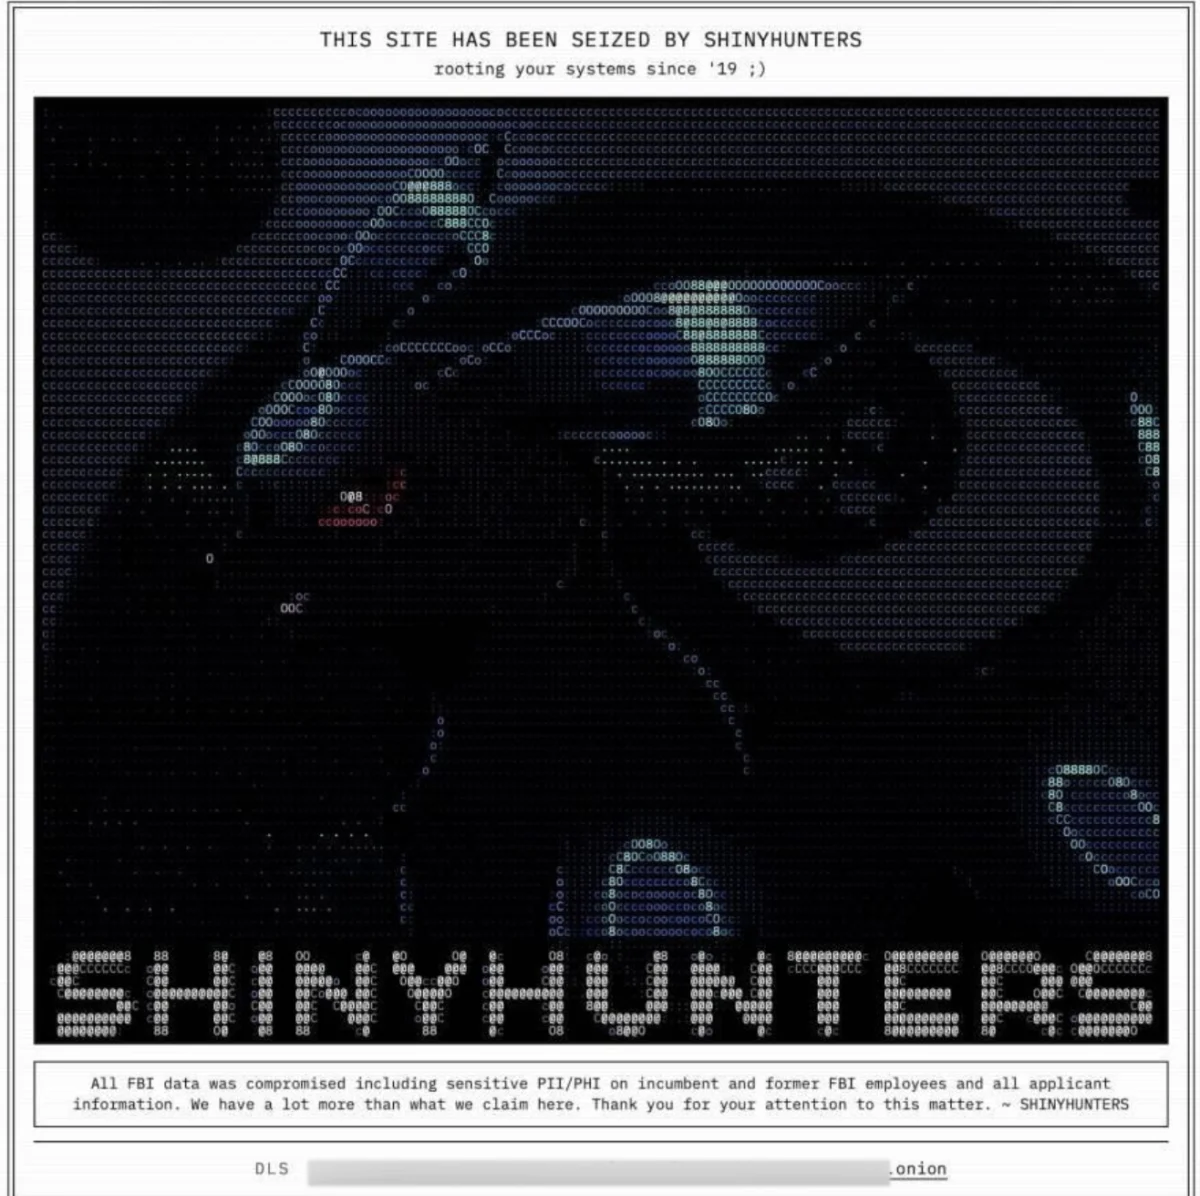
The arrest of Van der Stap appears to have served as the catalyst for the group’s most aggressive maneuvers to date. Within days of his detention, ShinyHunters claimed responsibility for a brazen breach of the FBI’s recruitment portal, apply.fbijobs.gov. The breach exposed the Social Security numbers and personal identifiers of over 5,000 FBI personnel, including special agents and officials tasked with investigating foreign state-sponsored cyber threats. Security researchers at Mandiant and the Google Threat Intelligence Group (GTIG) confirmed that the group leveraged a zero-day vulnerability in Oracle’s PeopleSoft software (CVE-2026-35273) to facilitate these mass intrusions.
The Rise of "Rey" and the SLSH Coalition
The character of ShinyHunters’ operations shifted dramatically following an internal power struggle. Sources close to the investigation indicate that the group’s operations were effectively co-opted by a teenage hacker based in Amman, Jordan, known by the alias "Rey." Rey is a central figure in the ScatteredLapsussHunters (SLSH) coalition, an entity formed through the loose integration of remnants from Scattered Spider, LAPSUS$, and ShinyHunters.
The animosity between Rey and Van der Stap appears to be rooted in a failed partnership with the supply-chain hacking group TeamPCP. Earlier in 2026, these factions collaborated to monetize stolen credentials from global code supply chains. However, the partnership collapsed when Mandiant researchers infiltrated TeamPCP, causing the stolen data to be invalidated by major cloud providers like Microsoft and Amazon. While the groups blamed one another for the failure, reports suggest that ShinyHunters went rogue, unilaterally extorting victims without sharing proceeds with their partners. The inclusion of the "Umbreon" ASCII art in the FBI job site defacement is widely viewed by experts as a calculated attempt by Rey to frame the Dutch suspect for the high-profile breach, further complicating the legal landscape for Van der Stap.
Broader Implications for Cybersecurity and Corporate Infrastructure
The exploitation of the Oracle PeopleSoft vulnerability highlights a systemic weakness in global business infrastructure. PeopleSoft, a staple in human resources and payroll management, is utilized by thousands of enterprises worldwide. The ease with which ShinyHunters bypassed web application firewall (WAF) mitigations suggests a sophisticated understanding of network security protocols. According to Mandiant researcher Austin Larsen, the group’s 2026 activities have been extraordinarily lucrative, with projections indicating the collective could net nearly $100 million in extortion payments by the end of the year.

The reach of these hacks extends beyond mere data theft; it represents a significant intelligence failure. The exposure of medical and psychiatric files belonging to FBI staff creates a long-term counter-intelligence risk, as such data can be weaponized for blackmail or targeted recruitment by hostile nation-states.
Official Responses and Legal Developments
The Dutch police have maintained a firm stance against the group’s intimidation tactics. In a statement, law enforcement confirmed the arrest and noted that the suspect is scheduled to appear before the Rotterdam District Court. The gravity of the case increased significantly on September 29, when reports emerged from the Dutch outlet RTL indicating that investigators are looking into allegations that Van der Stap may have attempted to orchestrate murders abroad.
In Washington, the FBI has adopted a more aggressive posture. Brett Leatherman, assistant director of the FBI’s cyber division, released a video message addressing the ShinyHunters collective directly. "Arrests have a way of changing who is willing to talk, and seized infrastructure has a way of showing us who’s left," Leatherman stated. He warned that the bureau’s investigation is ongoing and urged members to surrender before their anonymity is compromised by further law enforcement action.
Forensic Analysis and Future Outlook
The case of Pepijn van der Stap serves as a stark case study in the risks posed by "grey-hat" professionals who straddle the line between legitimate security work and criminal enterprise. While Van der Stap claimed in a September 2026 interview that his primary motivation was the "collection and organization of data," his alleged involvement in extortion and potentially violent criminal conspiracies suggests a far more malicious intent.

As law enforcement agencies across the globe continue to collaborate, the pressure on the SLSH coalition is mounting. The disruption of infrastructure, coupled with the potential for international extradition, creates a precarious environment for those remaining in the group. For the cybersecurity community, the incident underscores the necessity of faster patching cycles and a more robust approach to third-party software management.
The fallout from the Odido and FBI breaches will likely be felt for years, as the victims face the long-term consequences of identity theft and the loss of operational security. With the Dutch police promising further disclosures following the suspect’s court appearance, the focus now turns to whether the arrest of Van der Stap will lead to the unraveling of the wider SLSH network or if the group, led by the enigmatic Rey, will continue its trajectory of high-stakes, high-impact cyber warfare. The case remains a landmark event, proving that even as hackers evolve their tactics and form complex international alliances, the digital footprint they leave behind remains the ultimate instrument of their undoing.
