

Security researchers from password manager provider LastPass and Delphos Labs have uncovered a complex, multi-layered malware distribution campaign that exploits search engine optimization (SEO) techniques to impersonate at least 40 prominent software brands. The malicious infrastructure relies heavily on fraudulent GitHub repositories designed to trick unsuspecting users into downloading dangerous payloads. Central to this campaign is a previously undocumented information-stealing trojan dubbed "Rapuncel," which is deployed alongside a legitimate Microsoft-signed kernel driver capable of weaponized defense evasion.
This sophisticated cyberattack highlights the evolving methodologies threat actors employ to bypass modern endpoint security solutions. By combining SEO poisoning, DLL sideloading, heavily inflated archive files to evade static analysis, and a certified kernel driver that systematically terminates 145 distinct security products, the campaign represents a significant escalation in targeted digital threats. Cybersecurity analysts warn that the utilization of validly signed software components complicates detection efforts and poses severe risks to both enterprise environments and individual users.
The Anatomy of the Attack Chain
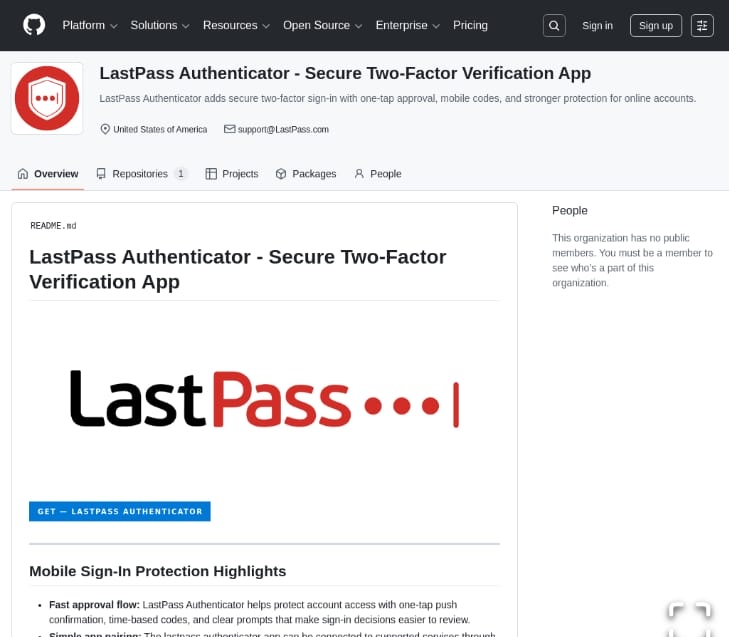
The genesis of the campaign begins with strategic SEO poisoning designed to manipulate search engine results pages. When potential victims search for popular software solutions—most notably tools like the LastPass Authenticator—they are steered toward convincing, yet entirely malicious, GitHub repositories. These repositories meticulously mimic official branding, documentation, and user interfaces to establish a false sense of security.
Once a user locates the download link on one of these fraudulent pages and initiates the process, they are routed through an intricate web of HTTP redirections. This redirection chain is engineered to obfuscate the origin of the traffic and frustrate automated security crawlers. Ultimately, the victim is directed to a payload-delivery server where they are served a ZIP archive. To outwit automated malware scanners and static analysis tools that often automatically discard or flag unusually small or standard-sized executables, the threat actors artificially bloat the file sizes of these ZIP archives up to a staggering 148 megabytes using padded data.
Upon extraction, the victim unwittingly executes what appears to be a legitimate utility. In practice, the installer is a repurposed copy of the Microsoft Visual Studio CoreCLR Debugger, known conventionally as vsdbg.exe. The malicious actors deliberately rename and configure this legitimate binary to execute a DLL sideloading attack. When the executable runs, it loads a custom, malicious dynamic-link library named vsdbg.dll. This DLL acts as the primary orchestrator for the subsequent deployment of both the Rapuncel infostealer and a highly destructive kernel driver designated as Alinubx.sys.
Weaponized Kernel Drivers and Defense Evasion
Perhaps the most alarming technical aspect of the campaign is the inclusion of the Alinubx.sys kernel driver. Disguised cunningly as a standard NVIDIA component bearing the name nvfsflt64.sys, the driver registers itself within the Windows operating system as the NvFsFilter service. Its primary function is to act as an aggressive Endpoint Detection and Response (EDR) and antivirus killer, sporting a hardcoded directory of 145 unique security product processes to systematically locate and terminate.
According to technical documentation released by LastPass, the driver leverages low-level operating system mechanics to achieve its goals. By invoking the kernel API function ObOpenObjectByPointer with the parameter AccessMode=KernelMode, the driver successfully bypasses standard user-mode security checks, specifically the SeAccessCheck path typically enforced during handle-open operations.
This methodology allows the driver to command the Windows kernel to open target processes directly as kernel-level code, affording it the privilege to terminate critical processes that would otherwise be shielded. Crucially, this technique defeats Protected Process Light (PPL)—a security architecture that many modern antivirus and EDR vendors rely upon to ensure their defensive agents survive even administrative-level tampering or termination attempts.
Compounding the threat is the provenance of the driver itself. Alinubx.sys is currently not listed on Microsoft’s vulnerable and malicious driver blocklist (ASR rules or HVCI blocklists). Instead, the specific driver variant utilized in this campaign was successfully signed through Microsoft’s official Windows Hardware Compatibility Publisher certificate chain, granting it implicit trust by the Windows operating system architecture.
Further analysis of Alinubx.sys by security researchers revealed that the driver possesses latent, highly advanced capabilities extending far beyond basic process termination. These include functionalities for file and registry hiding, arbitrary DLL injection, driver and process interception, network traffic manipulation, and port redirection. However, telemetry and forensic reviews indicate that these supplementary features remain dormant and are not actively invoked within the current operational scope of this campaign.
Inside the Rapuncel Infostealer
With the host machine’s protective defenses effectively dismantled and rendered inert by the Alinubx.sys driver, the Rapuncel infostealer initiates its data collection phase. The malware is engineered to sweep through the infected device, harvesting a wide variety of sensitive user data, credentials, session tokens, and system information.
To extract valuable credentials stored inside modern web browsers such as Google Edge and Google Chrome, Rapuncel must navigate around Google’s robust app-bound encryption mechanisms. To achieve this, the infostealer injects a specialized helper DLL directly into the target browser application, subsequently invoking its own custom Elevation Service to decrypt and harvest protected data streams.
Once the compilation of stolen data is complete, Rapuncel compresses the harvested files into a single archive. This archive is then exfiltrated to an external command-and-control endpoint residing at the IP address 2.26.126[.]50. The transmission is executed via raw TCP connections utilizing manually formatted HTTP requests, blending the outbound traffic to avoid standard HTTP inspection heuristics.
To ensure long-term persistence, Rapuncel registers itself as an official Windows service. This configuration allows the infostealer to survive system reboots. Furthermore, if a terminated security product manages to automatically restart or reactivate following a system event, Rapuncel’s persistent service immediately triggers the kernel driver to execute another round of terminations, keeping defensive software permanently suppressed.
Attribution and Threat Intelligence Assessment
Security researchers from LastPass and Delphos Labs have conducted extensive forensic comparisons of the infrastructure, code structure, and deployment mechanisms associated with the campaign. Based on their findings, analysts have assessed with moderate confidence that Rapuncel shares strong architectural and behavioral ties with BoryptGrab, a known infostealer family. Additionally, reverse-engineering efforts revealed that the loaders utilized to distribute the malware were constructed using the Cruciferra PUROSANGUE crypter, pointing to the accessibility of modular criminal toolsets on underground forums.
The breadth of the campaign—targeting upwards of 40 distinct software brands beyond just LastPass—indicates a wide-net distribution strategy. By casting a broad net across various software categories, the threat actors maximize their chances of capturing credentials from high-value targets across diverse corporate and personal sectors.
Industry Implications and Recommendations
The emergence of the Rapuncel campaign and its reliance on a Microsoft-signed kernel driver highlights a persistent, systemic challenge in modern cybersecurity: the abuse of legitimate code-signing infrastructure. When malicious actors can leverage valid publisher certificates to inject code directly into the Windows kernel, traditional perimeter defenses and trust models face severe hurdles. While tech giants like Microsoft continuously update blocklists and revoke compromised certificates, the lag time between discovery, reporting, and remediation leaves a window of vulnerability for global enterprises.
In response to these findings, cybersecurity professionals and threat intelligence agencies have issued clear guidance for enterprise organizations and individual consumers alike. Users are strongly advised to exercise extreme caution when downloading software, strictly restricting downloads to official developer websites and verified portals.
Furthermore, users should actively avoid third-party software aggregators, unverified GitHub repositories promoting cracked or free versions of paid software, and exercise skepticism toward sponsored or promoted search engine results that often serve as vectors for SEO poisoning attacks. Organizations are urged to monitor their endpoint telemetry closely for anomalies related to unexpected kernel driver loading, unusual process termination chains, and unauthorized modifications to system services.
