

In a significant blow to the global cybercrime ecosystem, Google’s Threat Intelligence Group (GTIG) announced today that it has successfully dismantled a massive, sophisticated botnet known as XCPE. This clandestine network, which had compromised more than 1.3 million Android TV set-top boxes, functioned by turning unsuspecting consumer hardware into nodes for advertising fraud and illicit residential proxy services. By severing the command-and-control infrastructure used by the manufacturers, Google and its industry partners have not only neutralized the primary infection vector but have also disrupted the connectivity of an estimated 10 million additional compromised IoT devices, ranging from telehealth hardware to automated karaoke systems.
Anatomy of a Supply Chain Attack
The investigation centered on Videostrong Technology Co., a China-based manufacturer of consumer electronics. According to the GTIG report, Videostrong deliberately embedded malicious software—the "XCPE" malware—directly into the firmware of its Android TV boxes. This meant that the devices were compromised the moment a user connected them to the internet for the first time.
The malware’s primary function was to turn these set-top boxes into residential proxy nodes. In this model, the device’s internet connection is secretly rented out to third-party "residential proxy" providers. These services are highly sought after by cybercriminals, as they allow malicious traffic to appear as if it originates from a legitimate residential IP address. This anonymity is critical for conducting account takeover attacks, evading anti-fraud systems on e-commerce platforms, and performing large-scale web scraping for AI model training.
By monetizing the backdoors, Videostrong reportedly sold access to these devices to various criminal affiliates. Once an affiliate gained access to a box, they were able to load additional modular malware, effectively turning the devices into a multi-purpose platform for cyberattacks. Google’s legal action to seize the domains and servers associated with this operation effectively cut off the "mothership" controlling these devices, forcing the malware to go dormant.
A Chronology of Escalation
The discovery of XCPE is the culmination of years of escalating security threats within the Android IoT ecosystem. The timeline of this crisis began in earnest as budget-friendly, "no-name" Android streaming boxes flooded global markets, often marketed through social media influencers as a way to access pirated content for a one-time fee.

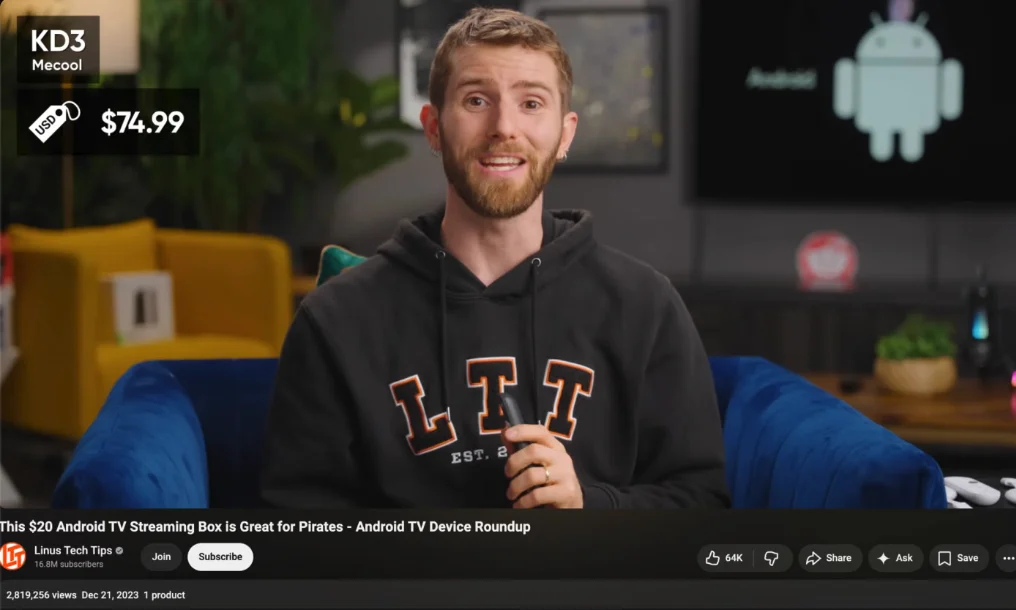
- 2023: Popular tech influencers, including the YouTube channel Linus Tech Tips, featured devices like the MECOOL box, inadvertently driving consumer adoption. While these channels have since updated their content to warn of the risks, the massive distribution of these devices laid the groundwork for the botnet’s expansion.
- January 2026: The cybersecurity firm Synthient published a landmark report on the "Kimwolf" botnet, which had begun using residential proxy vulnerabilities to jump from infected TV boxes to other sensitive devices on the same local networks, such as home computers and security cameras.
- July 2026: The FBI, in conjunction with international partners, seized hundreds of domains linked to NetNut, a residential proxy provider operated by the Israeli company Alarum Technologies. The operation revealed that NetNut had been operating a secondary botnet called "Popa," which specifically targeted TV boxes.
- October 2026: Following a $130 million funding round, the residential proxy provider Oxylabs rebranded as "Source," further highlighting the immense capital flowing into the industry that feeds these botnets.
- November 2026: Google’s GTIG officially publishes its findings on the XCPE botnet, identifying the deep-rooted collaboration between device manufacturers like Videostrong and Skyworth Technology (the maker of MECOOL boxes) and the proxy providers.
The Role of Residential Proxy Providers
The GTIG report identifies a troubling symbiotic relationship between hardware manufacturers and residential proxy services. These services provide software development kits (SDKs) that are integrated into the malware. The list of providers implicated in the XCPE ecosystem is extensive, including names such as AppSalt (Honeygain), NetNut, EarnFM, Traffmonetizer, Jaguar, LINKFOG, BMW/IPWeb, and GaGaNode.
The business model of these proxy providers relies on a vast, distributed network of IP addresses. While some providers claim to compensate users for their bandwidth, the XCPE botnet represents a more sinister variant: "zero-consent" monetization. Users have no idea their bandwidth is being sold, and they receive no compensation for the security risks or the data consumption associated with hosting criminal traffic.
Synthient’s research suggests that the 1.3 million figure provided by Google is likely a conservative estimate. Ben Brundage, founder of Synthient, noted that the modular nature of the malware means that once a device is compromised, it can be repurposed for multiple concurrent campaigns. The infrastructure discovered by investigators suggests that the total number of devices currently acting as proxy nodes is likely in the tens of millions.
The Broader Implications for IoT Security
The XCPE takedown highlights a systemic failure in the current IoT supply chain. Despite Google’s stringent compatibility and security testing requirements for Android, manufacturers like Videostrong found ways to bypass these checks by injecting the malicious code post-boot. This "security-by-default-broken" model presents a massive challenge for consumers who lack the technical expertise to inspect firmware or monitor network traffic.
Furthermore, the involvement of the Motion Picture Association (MPA) underscores the shift in how the entertainment industry views these devices. Beyond the copyright infringement issues inherent in "pirate" streaming boxes, the MPA and other studios are increasingly concerned with how these devices are being used to facilitate large-scale content scraping, which undermines the value of legitimate streaming services and digital media.
The risk is not merely financial. Because these devices reside on local home and office networks, they serve as a beachhead for attackers to move laterally. A compromised karaoke machine or smart signage system can be used to scan local area networks for vulnerabilities in PCs, NAS drives, or sensitive healthcare devices. The "Kimwolf" and "XCPE" incidents demonstrate that a single cheap streaming box can act as a gateway to an entire household’s digital life.

Moving Forward: Accountability and Regulation
Google’s actions, while decisive, serve as a reminder that the responsibility for secure hardware cannot rest solely on the OS developer. The fact that manufacturers were willing to intentionally infect their own users for a share of the proxy rental profits indicates a need for stronger international regulations and more aggressive consumer protection enforcement.
Publicly traded entities involved in the supply chain, such as Skyworth Technology and Alarum Technologies, are facing mounting pressure from both regulators and investors. The valuation of companies like Source—which reached $3.6 billion earlier this year—raises questions about the due diligence performed by private equity firms when investing in the proxy industry.
For the average consumer, the lesson is stark: "smart" devices that appear too good to be true—often promising unlimited free access to premium content—are almost certainly being subsidized by the theft of the user’s own digital privacy and network bandwidth. Experts recommend that users audit their home networks for unknown traffic, ensure that IoT devices are placed on segregated VLANs where possible, and avoid purchasing streaming hardware from unverified, low-cost vendors.
As the XCPE botnet is dismantled, the industry must now contend with the "zombie" hardware left in its wake. While the command-and-control servers are down, the malicious firmware remains on the devices. Without a coordinated effort to push firmware updates or recall these units, the hardware remains vulnerable to future exploitation by other threat actors. The takedown is a victory, but the battle to secure the consumer IoT landscape is far from over.
